Chinese Hackers Deploy CLEANGULP via Chrome Zero-Day Chain
Researchers identified a campaign using unpatched Chrome and Windows flaws to infect government targets with new malware.
Key points
- Chinese hackers exploited three zero-day vulnerabilities in Chrome and Windows to deploy the CLEANGULP malware.
- The attacks targeted government entities using fake websites that mimicked reputable media and NGO organizations.
- The malware provides attackers with the ability to run commands, transfer files, and maintain persistent access to systems.
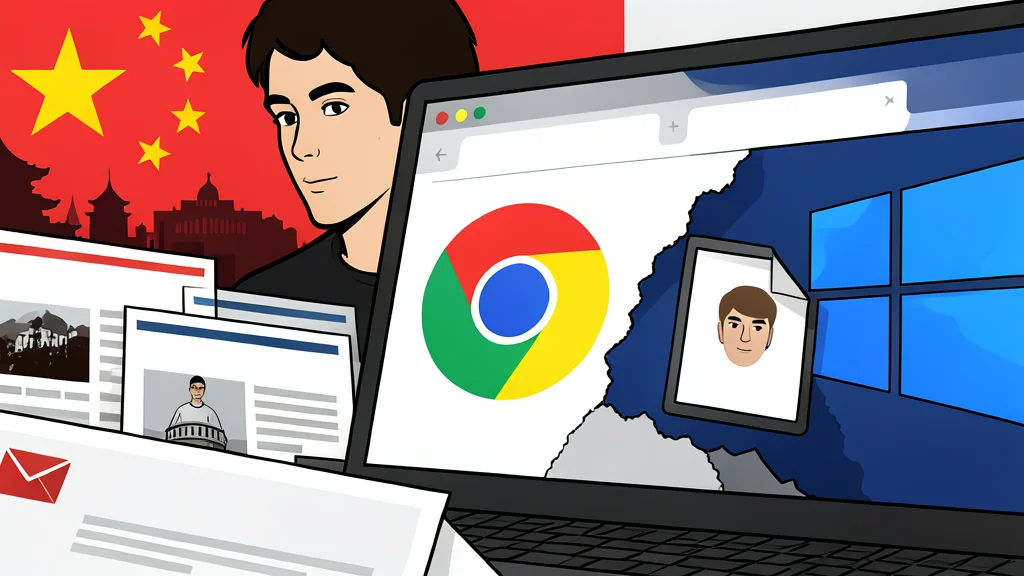
A Chinese state-linked threat actor has exploited a chain of recently disclosed vulnerabilities in Google Chrome and Microsoft Windows to deploy new malware. The attacks, detected in early September 2026, leveraged three specific flaws that allowed attackers to escape the browser’s security sandbox and execute code on the victim's machine.
The malware, dubbed CLEANGULP, was delivered through deceptive websites mimicking media outlets and non-governmental organizations. According to The Hacker News, the campaign primarily targeted government entities in Asia, using phishing emails to lure victims into clicking links that triggered the exploit chain.
Exploitation of unpatched browser flaws
The attack vector relied on a specific combination of two Chrome vulnerabilities and one Windows component flaw. By chaining these bugs, the attackers bypassed the browser's isolated environment, which is designed to contain malicious code. This allowed them to gain full remote code execution capabilities on the host system without the user installing any additional software.
The exploit kit used in these campaigns, identified as BlueMoon, was observed in multiple incidents. Researchers noted that this specific combination of flaws was not previously seen in the wild before these recent attacks, indicating that the vulnerabilities were being exploited as zero-days before patches could be widely applied.
Deceptive lures target government officials
The threat actor, identified as UTA0565, used sophisticated social engineering tactics to deceive recipients. Emails were crafted to appear as if they came from reputable organizations like the Center for American Progress or China Digital Times. The messages often urged recipients to support political causes or activists, creating a sense of urgency that prompted clicks on spoofed links.
Once the link was clicked, the victim was redirected to a fake website that looked identical to the legitimate source. Hidden within the page was an iframe that loaded the exploit kit. This method allowed the attackers to maintain the illusion of legitimacy while silently executing malicious code in the background.
Malware capabilities and command control
The CLEANGULP payload is a command-and-control tool that gives attackers extensive control over the infected machine. It can execute shell commands, list running processes, and transfer files to or from the system. These capabilities suggest the malware is intended for long-term surveillance and data exfiltration rather than destructive ransomware attacks.
The malware communicates with a hard-coded domain that closely resembles a well-known non-profit media outlet. This mimicry helps the malicious traffic blend in with legitimate web requests, making it harder for network defenders to detect the command-and-control channel. The use of this specific infrastructure indicates a coordinated effort to maintain stealth and persistence.