Telegram Export Flaw Lets Hidden Scripts Steal Chat Data
A vulnerability in Telegram Desktop allowed hidden code to be embedded in chat exports, enabling attackers to steal message histories when users opened specific files in a browser.
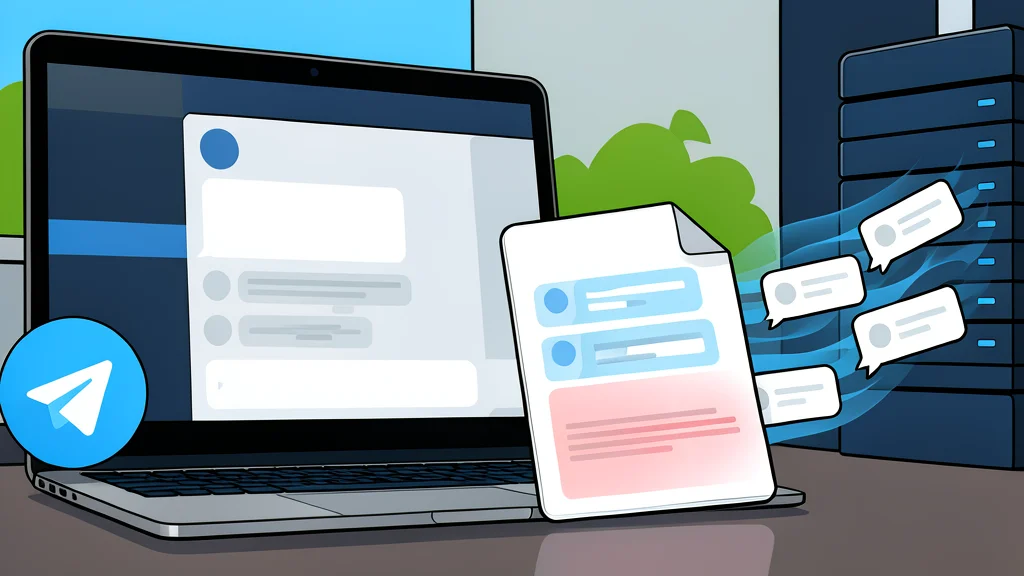
A security flaw in Telegram Desktop allowed attackers to hide malicious JavaScript inside chat messages that users later exported to HTML files. According to a report by The Hacker News, this vulnerability let a bot plant code that remained invisible within the application but executed once the exported file was opened in a web browser. The script could then copy every message in that file to an attacker-controlled server or rewrite what the page displayed.
The issue stemmed from how Telegram Desktop handled data escaping during the export process. While the application protected message text and sender names from being interpreted as code, it failed to apply the same safeguards to button labels attached to bot messages. This oversight meant that a bot could embed a script tag in a button's text, padded with invisible characters so the button appeared empty to the user. Once the export was generated, the hidden code was ready to run.
Hidden Code in Button Labels
Security researchers Denis and Aleksander Rostilov identified that the export code wrote button text directly into the HTML page without neutralizing special characters. In standard web development, this process, known as escaping, converts symbols like angle brackets into plain text so browsers do not treat them as instructions. Because this step was skipped for button labels, a malicious bot could inject a script that remained dormant inside the Telegram app but became active in the browser environment.
The trade-off here involves convenience versus security. Telegram Desktop offers a robust feature to save chats as readable HTML pages, which is useful for archiving or sharing. However, this feature relied on the assumption that all input fields would be sanitized equally. The researchers found that the bot did not even need to be a member of the target chat. If a user forwarded a message containing the hidden script, the code traveled with it, sitting in the chat history until it was eventually exported.
Limited Data Exposure Per File
When an affected export file was opened, the script ran automatically without requiring any further user interaction. It could read every message within that specific file, including sender names, timestamps, and the chat's metadata, and send them to an external server. The scope of the leak was contained by the application's design, which splits long exports into separate files of 1,000 messages each. Therefore, one compromised file exposes only its own contents rather than the user's entire account or unrelated chats.
Beyond data exfiltration, the script could also alter the appearance of the export. In the researchers' demonstration, the code replaced the chat history with a fake verification form, a technique often used in phishing attacks. It could also modify dates, senders, or message text within the file. While this did not change Telegram's server-side copy of the chat or the original file on the user's disk, it compromised the integrity of the export as a record.
Fix Released But Old Files Risky
Telegram addressed the issue in a patch released in July, adding the missing escaping logic to prevent script injection. The fix was included in version 6.9.4 beta and later in the 7.0.1 stable release. However, a significant catch remains for users: updating the app does not sanitize HTML files that were already exported using earlier, vulnerable versions. Those old files can still carry the malicious script and will execute it if opened in a browser with JavaScript enabled.
The risk is conditional on three factors: the export must have been created before the fix, the message containing the script must be part of that specific chat export, and the file must be opened in a browser that allows JavaScript. The researchers noted that they tested the flaw only on their own accounts and did not find evidence of real-world exploitation. Nevertheless, users with old HTML exports from Telegram Desktop should be cautious, as the danger lies in the static file rather than the live application.